Teenage Ransomware Kingpin Arrested Amid Pentagon Data Breach
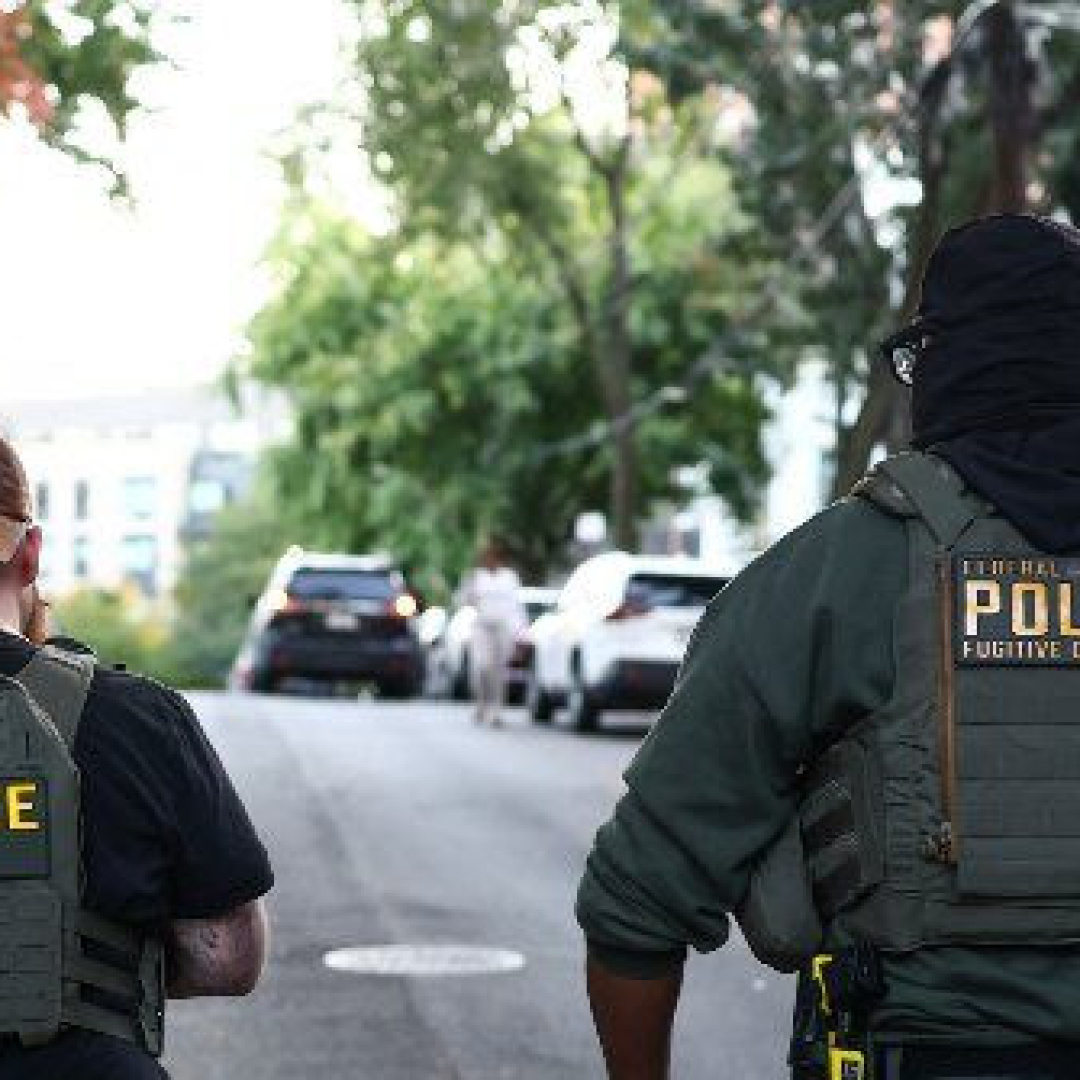
In a week marked by alarming cybersecurity incidents, Europol announced the arrest of a 16-year-old identified as the leader of KillSec, a ransomware group linked to a spree of international extortion and data theft. This revelation underscores a disturbing trend where even the youngest among us can wield significant power in the cybercrime arena. The arrest coincided with the FBI's announcement of detaining a hacker associated with ShinyHunters in Jordan, who was implicated in a data breach that the FBI attributed to a contractor's failure to update software with a known vulnerability.
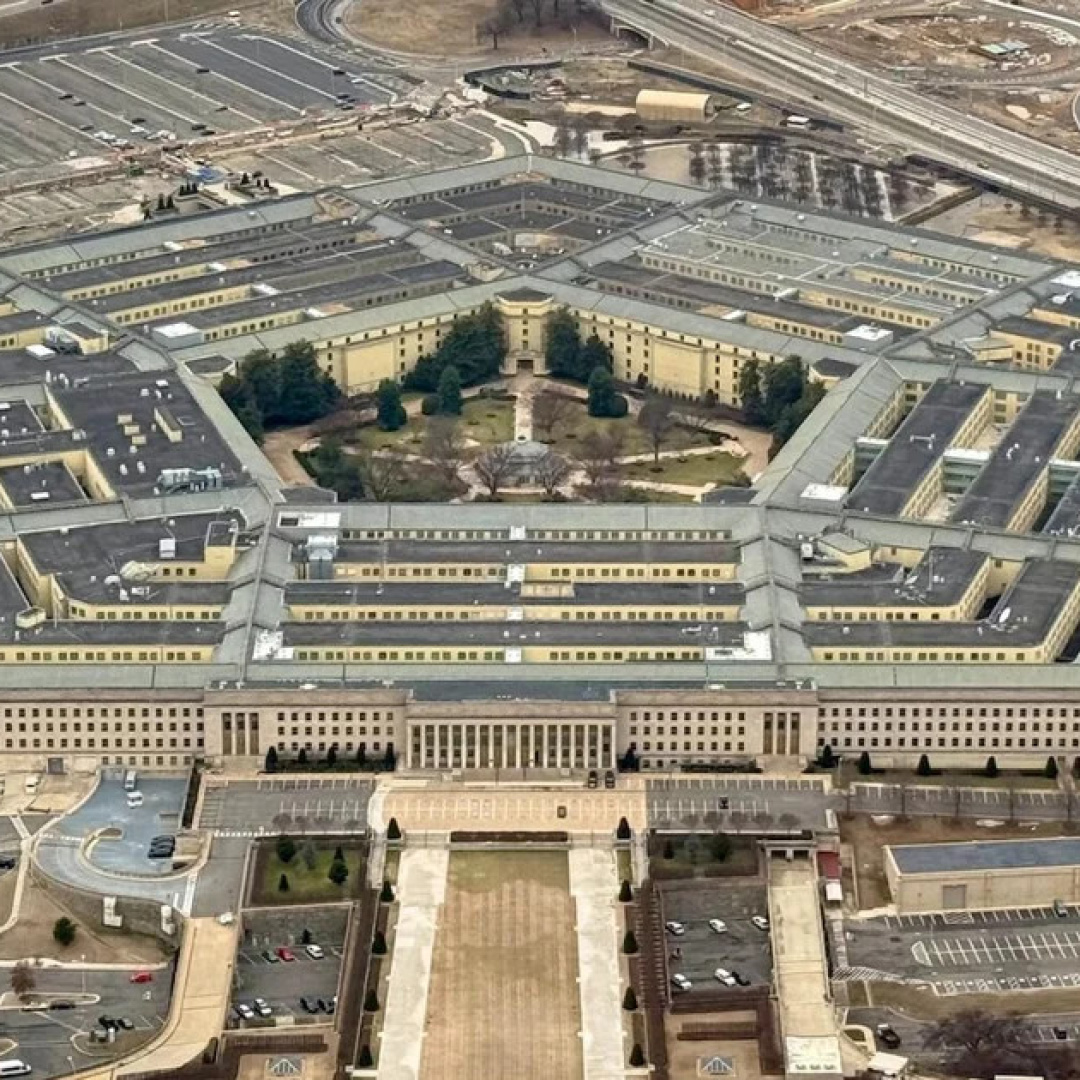
Meanwhile, the U.S. Department of Defense disclosed a significant breach of personnel records at the Defense Manpower Data Center (DMDC), where attackers accessed sensitive information, including Social Security numbers, military service records, and personal details of millions. Reports indicate that the attackers had access to the servers storing this unencrypted data for several months, from October 2025 to July 2026, raising serious questions about the Pentagon's data security protocols. As a result, approximately 2.76 million living individuals, including current and former defense personnel, had their data compromised, alongside records of 294,000 deceased individuals. The Department of Defense is reportedly reaching out to those affected, offering credit monitoring services, but the potential for misuse of this data extends beyond mere identity theft.
Common Sense Shop
The United States of Common Sense
Amazon shopping links. Sponsor Complete!
The implications of such breaches are profound. Data collected on defense personnel can be invaluable for adversaries seeking to undermine national security. As the Pentagon grapples with this incident, the question remains: how can such a critical institution allow its data to remain unprotected for so long? The breach is not an isolated incident; it reflects a broader trend of inadequate cybersecurity measures across various sectors.
In another troubling development, South Korean financial institutions, including Shinhan Bank and Kookmin Bank, reported data breaches affecting tens of thousands of customers. The Financial Services Commission (FSC) of South Korea convened an emergency meeting to address these attacks, which appear to be driven by data theft rather than financial gain. The use of AI tools in these attacks highlights the evolving nature of cyber threats, where hackers leverage advanced technologies to exploit vulnerabilities.
Urgent Need for Enhanced Cybersecurity Measures
As these incidents unfold, it is clear that the landscape of cybersecurity is fraught with challenges. The need for robust security measures and proactive responses has never been more urgent. With hackers increasingly targeting sensitive data, institutions must prioritize cybersecurity to safeguard their information and maintain public trust.
The Common Sense Test
In light of these developments, it is essential for individuals and organizations alike to remain vigilant. The rise of cybercrime, particularly among younger offenders, should serve as a wake-up call for all stakeholders in the cybersecurity realm. The responsibility to protect sensitive data lies not only with organizations but also with individuals who must practice good internet hygiene to mitigate risks.
As we reflect on these events, it is crucial to ask: what measures are being taken to address these vulnerabilities? The arrest of a teenage ransomware kingpin and the Pentagon's data breach should prompt a reevaluation of our cybersecurity strategies. We must demand accountability from those in charge of safeguarding our data and ensure that robust protections are in place to prevent future breaches. The stakes are high, and the consequences of inaction could be dire for national security and individual privacy.